GRE VPN Endpoint Migration
Tunnel0 is up/up on the new circuit and the far site is still unreachable. Find the half of the migration that was missed, live, right below.
Symptom
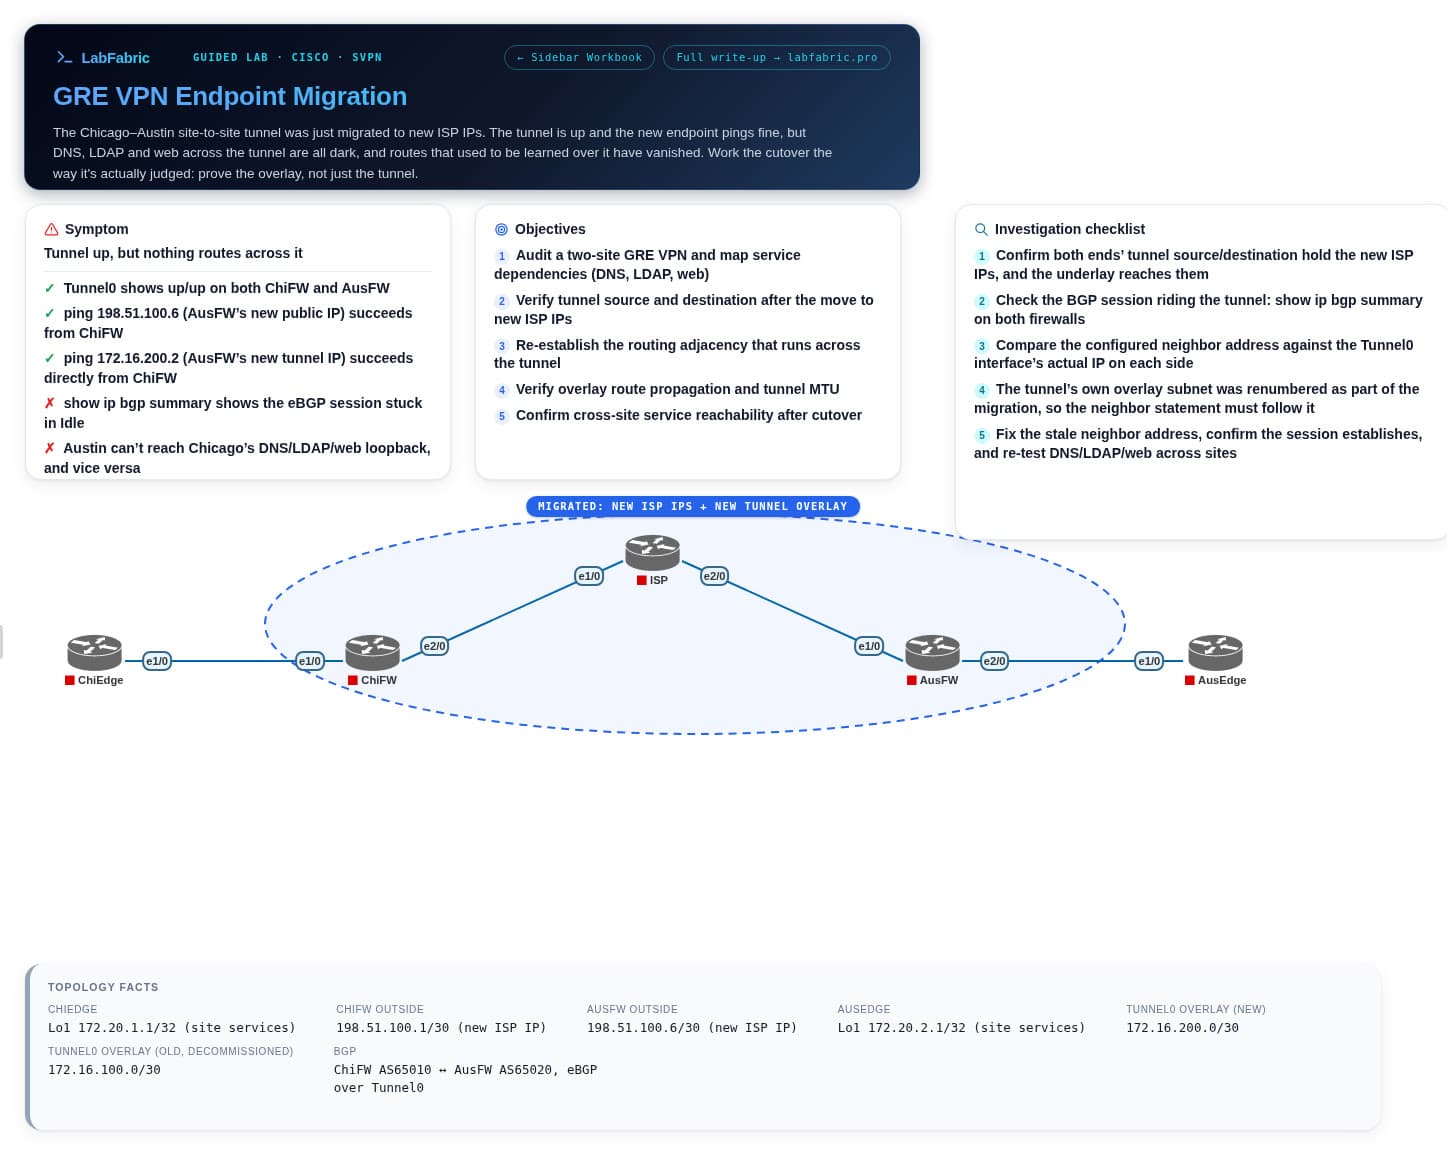
A site-to-site GRE tunnel has just moved to new ISP IPs. The tunnel is up, but DNS, LDAP and web across the two sites have gone dark.
Your mission
Inspect, recover, then verify
Format
Cisco IOS CLI
Investigate before you configure.
Use the CLI evidence to isolate the fault, make the smallest safe correction, then verify the network state changed.
Observe the symptom and link state.
Diagnose by comparing the protocol evidence.
Verify the expected device state and confirm the original symptom is resolved.
Console access: HQ · BRANCH
This workspace stacks for portrait phones. Rotate to landscape for the full split-screen console.
Need a hint?
Reveal the root cause when you're ready.
Try the investigation first, then use this as your escape hatch, not a dead end.
Create a free account to open GRE VPN Endpoint Migration. You get the root cause and the full step-by-step fix.
No spam. The fix lands in your inbox too. Your account includes 5 guided labs free. After that, the Learning Pass unlocks every remaining lab.
Lab debrief
Turn the session into a repeatable troubleshooting pattern.
Use this reference after your attempt: first explain the symptom, then verify the evidence, then confirm the repair.
The problem
After moving a site-to-site GRE tunnel onto new ISP IPs, the tunnel shows up and you can ping the new endpoint, but the remote site can't reach DNS, LDAP or web, and the routes that used to be learned over the tunnel have disappeared.
What you'll practice
- Audit the two-site GRE topology and find the loopbacks that stand in for each site's services
- Verify tunnel source and destination after the move to new ISP IPs
- Re-establish the routing adjacency that runs across the tunnel
- Verify overlay route propagation and tunnel MTU
- Confirm cross-site reachability between the service loopbacks after cutover
The topology
Two sites, Chicago and Austin, each with an edge router behind a zone-based firewall, connected across an ISP backbone by a GRE tunnel. Each site's DNS, LDAP and web services are represented by a loopback that is only reachable over the tunnel, so a mis-migrated endpoint shows up as unreachable services, not just a down interface.
Commands to run yourself
The real diagnostic commands for this lab, copy-paste ready. Run these in the same order to reproduce the investigation on your own session.
show interfaces Tunnel0show ip bgp summaryshow running-config | section router bgpTopology diagram
Inside a real session
More genuine captures from this lab running on the platform, at full size so the console text stays readable.
Rate this lab
No ratings yet
Fact-checked references
The commands and behaviour in this lab were checked against these primary references.
Frequently asked
Is the tunnel the problem, or the routing?
That's the lesson: the tunnel line-protocol can come up on the new IPs while the routing that rides over it never re-forms, so services stay dark until you fix the overlay, not the tunnel.
Does this map to SVPN?
Yes. Site-to-site tunnel configuration, migration and troubleshooting are core Cisco Secure VPN (SVPN) topics, exercised here on a real dual-site topology.
Ready to run this lab yourself?
No setup, no image sourcing. Book a session or ask for a live demo.